
🌐 Also available in: Deutsch · Français · Español
It’s the First Advent, which means the season of warm lights, cinnamon smells, questionable sweaters, and…
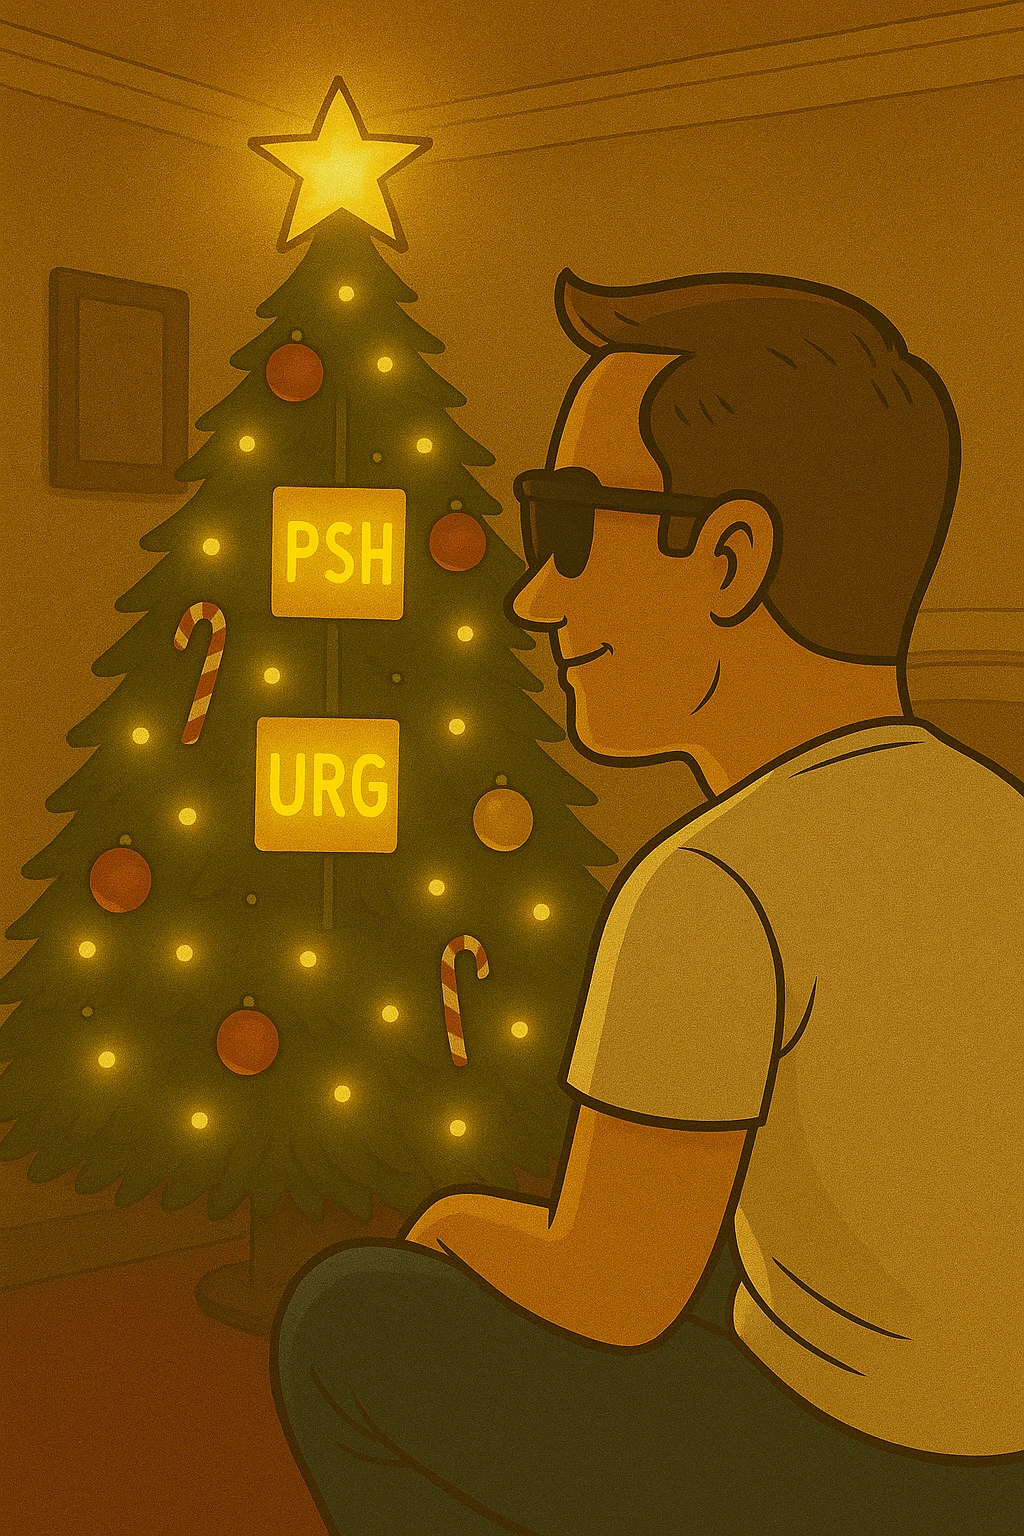
TCP packets dressed up like Christmas trees.
Because while normal people light candles,
we — the blessed, overcaffeinated nerds of the internet —
light flags.
🎄 What in Santa’s name is an XMAS Scan?
Imagine Santa gets bored, hacks into the North Pole mainframe, and decides to sneak around without making noise.
Instead of knocking on doors (SYN packets), he sends out little packets decorated with ALL the shiniest flags:
- FIN — “I’m done, but not really 🎁”
- PSH — “Open up, I brought cookies 🍪”
- URG — “This is super important. Like, priority-candy-delivery important 🔔”
Put together, these flags light up like a nerd’s Christmas tree after a bulk order of RGB LEDs.
Hence the name:
XMAS Scan — because it sparkles weirdly and nobody normal understands why.
🎅 How does it actually work?
Normal TCP communication is polite. It says:
“Hello, may I establish a connection?”
“Why yes, dear packet, you may.”
XMAS packets, on the other hand, roll in wearing blinking lights, yelling:
“SURPRISE PACKAGE DELIVERY! 🎁🎁🎁”
And depending on how the host reacts, you can tell:
- If the port is open:
→ The system stays quiet, pretending it’s not home.
(Much like your neighbor when you ask for help carrying IKEA furniture.) - If the port is closed:
→ It sends back a RST (“Reset”), basically saying:
“Buzz off, weird packet!”
Elegant. Festive. Questionably RFC-compliant.
🧦 Why do people use XMAS scans?
Because nerds like doing things in the most overcomplicated way possible.
Traditionally, XMAS scans were used to:
- Slip past old firewalls
- Confuse ancient IDS systems
- Perform stealthy reconnaissance
Today, most modern systems respond with the digital equivalent of:
“Nice try, Rudolph.” 🚫🦌
🔥 How to launch one (for legal, ethical, Santa-approved testing!)
nmap -sX your.target.here
It’s basically like sending the Grinch down someone’s chimney, but in a socially acceptable cybersecurity way.
🕯️ A warm Advent reminder…
As we light the first Advent candle, may we also remember to:
- Patch our servers
- Check our firewalls
- Monitor unusual traffic
- And laugh at bots tossing weird packets at port 80 like confused reindeer
Because nothing says “Christmas spirit” quite like:
\x16\x03\x02\x01\xA0\x00\xFF\xPSH\xFIN\xURG
An XMAS scan lights up all TCP flags like a nerdy Christmas tree, making it a classic trick for stealthy nmap port probing.
To keep your server from getting holiday-themed portscans, you can simply drop any packet with every flag set.
The following iptables rule acts like the Grinch and blocks those festive intrusions instantly:
/sbin/iptables -A INPUT -p tcp --tcp-flags ALL ALL -j DROP
Clean, effective, and perfectly suited for anyone who prefers their Christmas lights on the tree—not in their packet headers.
Peace on Earth.
Goodwill to sysadmins.
May your logs be clean and your packets festive.
🎄✨ Merry Nerdmas, everyone! ✨🎄


